AI Governance
The rules your agents run under, written for your regulators.
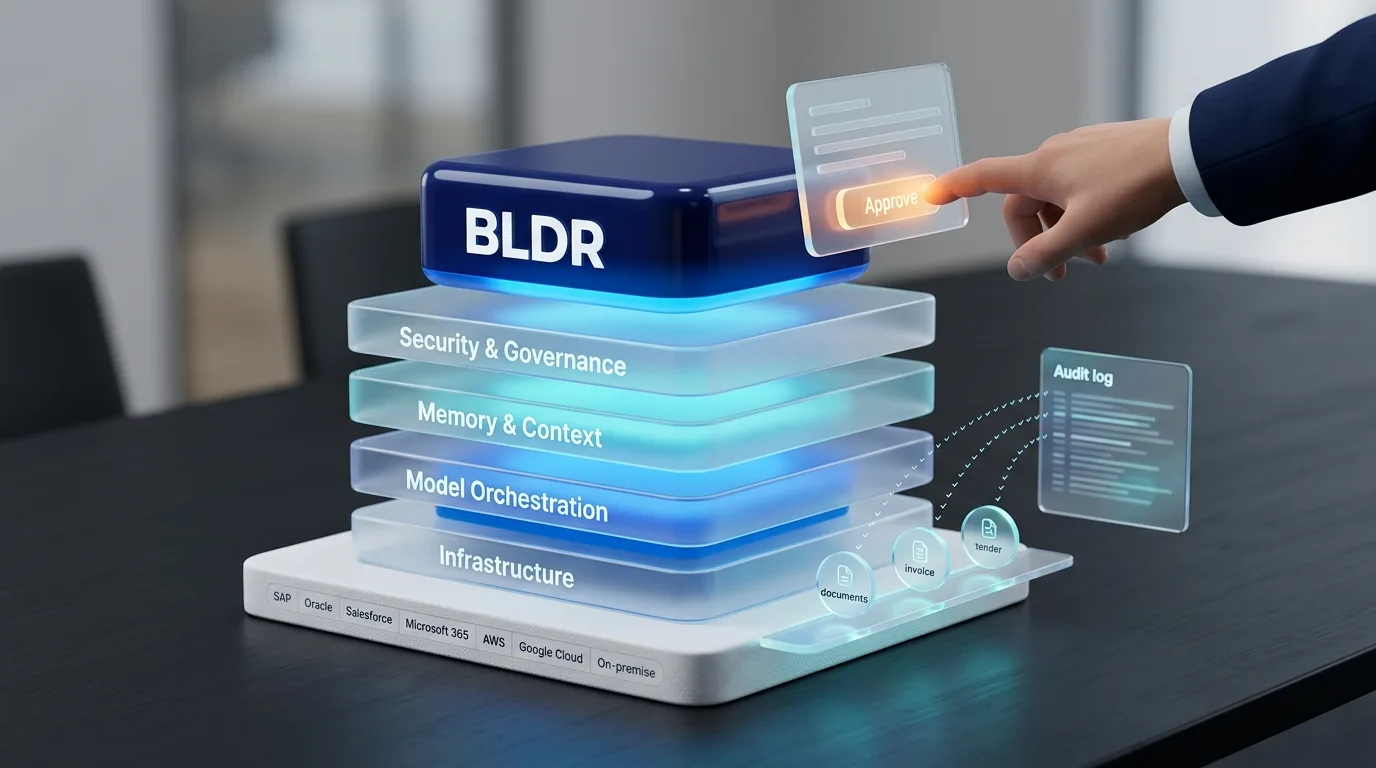
Agents act. Governance decides what they may do, with which data, and who approves it. We design the policy, controls and approval paths, then configure them in BLDR so the rules aren't just a PDF.
What you get
- AI policy. Acceptable use, data classes, model choices and who decides.
- Approvals and human-in-the-loop. Which actions need a person, and how a person takes over.
- Shadow AI programme. A governed alternative staff will use, clear policy and logging of every use.
- Regulatory alignment. Mapped to Saudi PDPL, NCA controls and SAMA where relevant, the UAE PDPL, Australia's Privacy Act, and the EU AI Act for European operations.
- Audit trail requirements. What must be logged, kept and reported, and to whom.
How it runs
- AssessCurrent AI use, including the unofficial kind.
- DesignPolicy, roles, approvals and data rules.
- ConfigureThe rules built into BLDR's gateway and approvals.
- ReviewA regular review as agents and rules change.
Built for governed enterprise AI
Sovereign by design. Ready for your auditors.
Security, privacy and deployment readiness, set out clearly for your security, legal and procurement teams. Every control is documented in our security pack. Request the security pack
ISO 27001Security management alignment
SOC 2 ReadyControls-ready posture
GDPRPrivacy-aware workflows
Privacy Act (AU)APP and ADM-ready logging
PDPL and NCASaudi data and cyber controls
Sovereign-ReadyLocal and controlled deployment
The sovereign agent OS
Build, govern and run AI agents across every system you own, inside your walls and your country.
Talk to the company behind BLDR.
Briefings for boards, CIOs and procurement teams, in Sydney, Dubai and Riyadh.